SOC 2 Type II
Externally audited security controls, renewed annually since 2023.
Audited by an external SOC 2 auditor every year since 2023. Built and operated in the EU. Run in our cloud or in yours.
Externally audited security controls, renewed annually since 2023.
Full visibility into access and activity, human and agent access alike, in production at Synchrony, one of the largest US consumer banks.
Built and operated in the European Union, under the General Data Protection Regulation.
Isolated operation in your own cloud environment for the highest security requirements, as run in production on AWS at a global printing services company.
Connects to your identity infrastructure, with automated user provisioning via SCIM; local user management where SSO isn't wanted.
Permissions derived automatically from metadata values, in production across a large part of our customer base, up to a permission complexity far beyond asset-by-asset management (see the Arper case).
Customer data is encrypted where it is stored and travels only over encrypted protocols.
Requests are inspected and filtered before they reach the platform.
Previews and renditions are served from edge locations close to your audiences.
Sized for very high asset and user counts, so portals stay available as audiences grow.
Current and past availability, published at status.smint.io.
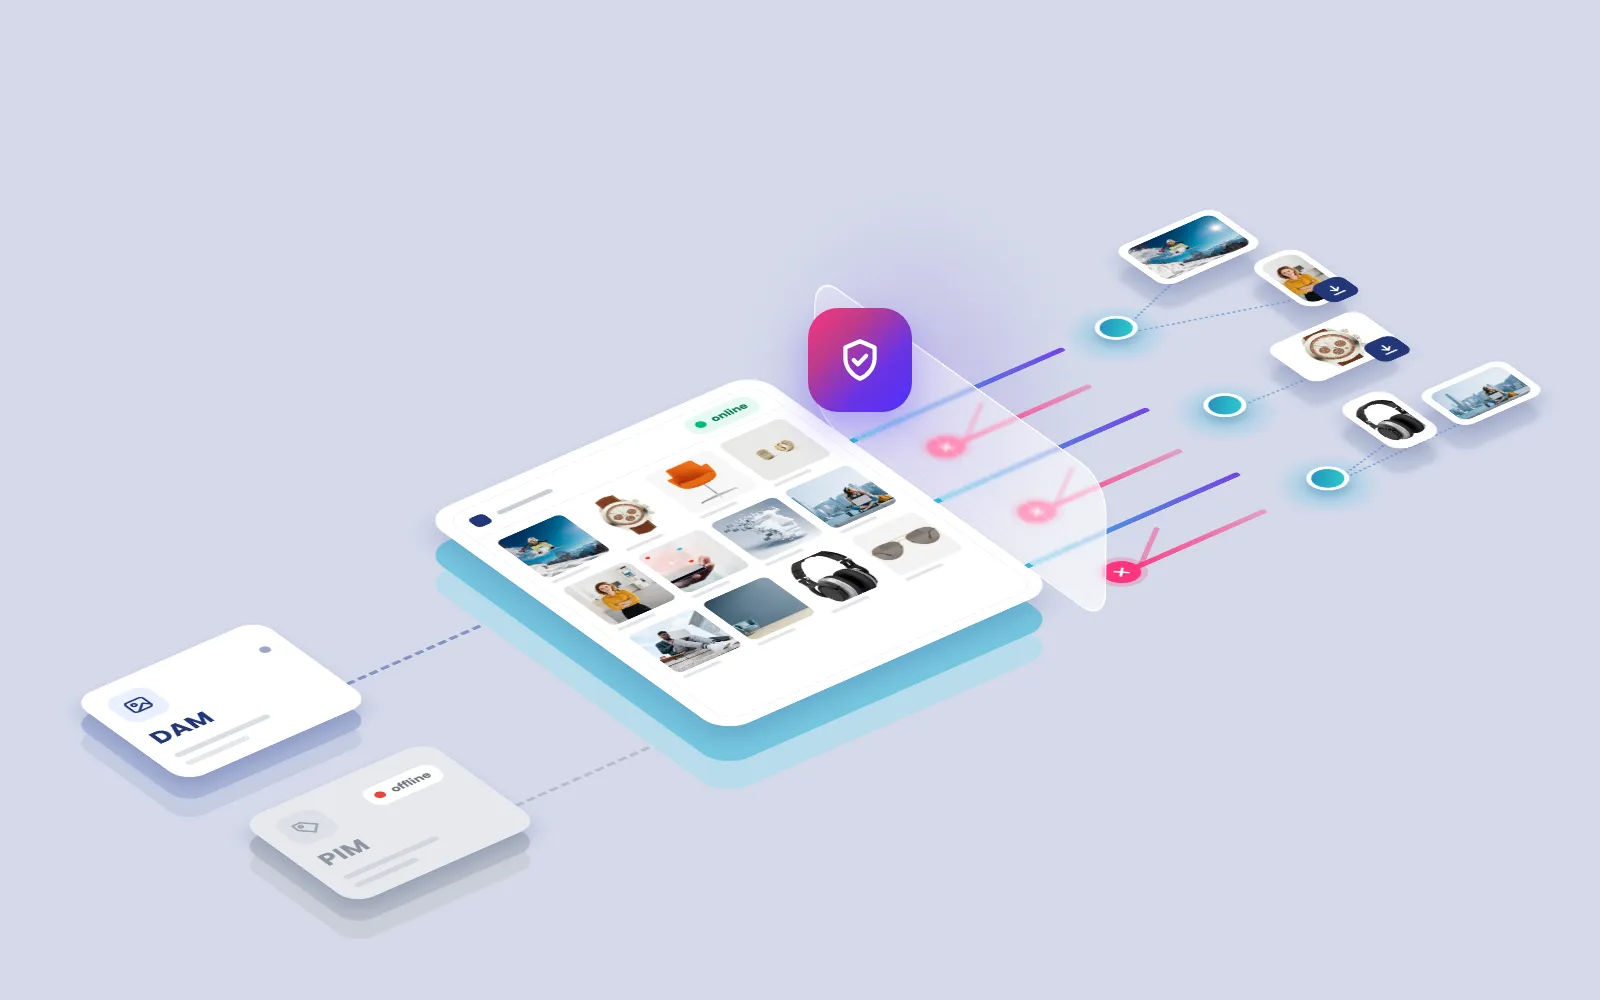
Your management systems remain the system of record.
The controls below are what the SOC 2 auditor checks every year. They cover the software, the people who build it, and the systems it runs on.
Developed, implemented and maintained to protect the security, integrity and confidentiality of the platform and its data. Risk assessments cover internal and external threats.
The development process is designed to detect security issues during the software lifecycle. Regular security assessments, penetration tests and vulnerability scans come on top.
Data processing systems are protected from unauthorized access, with phishing-resistant authentication factors and carefully managed employee access to applications and data.
Every employee is trained in security during onboarding and in regular courses covering the current threat landscape, attack vectors and principles. All company devices are centrally managed, with mobile device management and anti-malware protection.
Protected from unauthorized access, use, modification, disclosure, destruction or loss. Encrypted at rest, and transferred between our services and to users only over secure, encrypted protocols.
Systems are updated regularly to close vulnerabilities. Security incidents and events are identified and remediated.
Least privilege: access is limited to those with a legitimate business need. Consistency: security controls apply across all areas of the company, not just the product. Defense in depth: multiple layers of controls create redundancy if a single measure fails. Gradual implementation: controls mature iteratively, toward more effectiveness, more auditability and less friction.
Delivery runs on a secure global content delivery network. Previews, renditions and downloads are served close to your audiences.
In front of it sits a web application firewall. Requests are filtered before they reach the platform.
Behind both, audience traffic is answered from the platform's own index, never from your systems. They keep their API capacity, and portals stay up even when a source system is down.
Smint.io is a company based in the European Union, in Linz, Austria, and operates in compliance with the EU General Data Protection Regulation, alongside all legal and regulatory requirements related to security. Threats change, and so do our controls. Every employee is expected to know the risks and to help protect our systems.
SOC 2 report, security documentation, deployment options and SSO details are available on request, early in the process.